Communications

Zuckerberg Plans To Integrate WhatsApp, Instagram and Facebook Messenger (nytimes.com) 126

Mark Zuckerberg, Facebook's chief executive, plans to integrate the social network's messaging services -- WhatsApp, Instagram and Facebook Messenger -- asserting his control over the company's sprawling divisions at a time when its business has been battered by scandals.

The New York Times: The move, described by four people involved in the effort, requires thousands of Facebook employees to reconfigure how WhatsApp, Instagram and Facebook Messenger function at their most basic levels. While all three services will continue operating as stand-alone apps, their underlying messaging infrastructure will be unified, the people said. Facebook is still in the early stages of the work and plans to complete it by the end of this year or in early 2020, they said.

Mr. Zuckerberg has also ordered all of the apps to incorporate end-to-end encryption, the people said, a significant step that protects messages from being viewed by anyone except the participants in the conversation. After the changes take effect, a Facebook user could send an encrypted message to someone who has only a WhatsApp account, for example. Currently, that isn't possible because the apps are separate.

Chrome

Chrome API Update Will Kill a Bunch of Other Extensions, Not Just Ad Blockers (zdnet.com) 93

An anonymous reader writes: A planned update to one of the Google Chrome extensions APIs would kill much more than a few ad blockers, ZDNet has learned, including browser extensions for antivirus products, parental control enforcement, phishing detection, and various privacy-enhancing services. Developers for extensions published by F-Secure, NoScript, Amnesty International, and Ermes Cyber Security, among others, made their concerns public today after news broke this week that Google was considering the API change. Furthermore, efforts to port NoScript from Firefox to Chrome are also impacted, according to the plugin's author, who says the new API update all but cripples the NoScript for Chrome port.
Security

How Web Apps Can Turn Browser Extensions Into Backdoors (threatpost.com) 34

"Threatpost has a link to some recent research about ways web pages can exploit browser extensions to steal information or write files," writes Slashdot reader jbmartin6. "Did we need another reason to be deeply suspicious of any browser extension? Not only do they spy on us for their makers, now other people can use them to spy on us as well. The academic paper is titled 'Empowering Web Applications with Browser Extensions' (PDF)." From the report: "An attacker [uses] a script that is present in a web application currently running in the user browser. The script either belongs to the web application or to a third party. The goal of the attacker is to interact with installed extensions, in order to access user sensitive information. It relies on extensions whose privileged capabilities can be exploited via an exchange of messages with scripts in the web application," researchers wrote. They added, "Even though content scripts, background pages and web applications run in separate execution contexts, they can establish communication channels to exchange messages with one another... APIs [are used] for sending and receiving (listening for) messages between the content scripts, background pages and web applications."

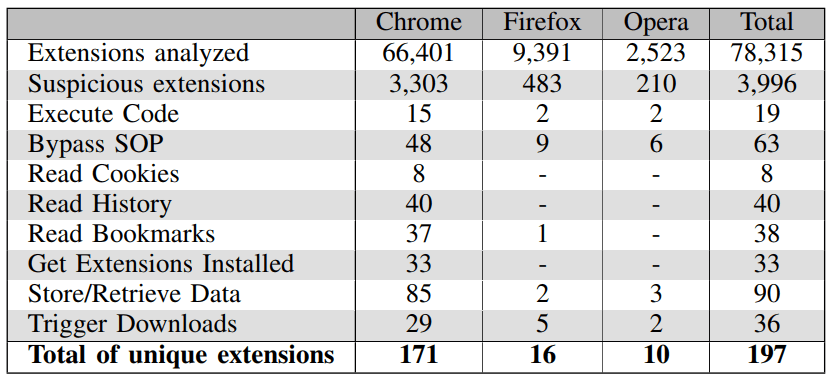
The researcher behind the paper focused on a specific class of web extension called "WebExtensions API," a cross-browser extensions system compatible with major browsers including Chrome, Firefox, Opera and Microsoft Edge. After analyzing 78,315 extensions that used the specific WebExtension API, it found 3,996 that were suspicious. While it seems voluminous, they noted that research found a small number of vulnerable extensions overall, and that concern should be measured. However, "browser vendors need to review extensions more rigorously, in particular take into consideration the use of message passing interfaces in extensions."

Security

France Will Hack Its Enemies Back, Its Defense Secretary Says (theregister.co.uk) 71

France's defence secretary Florence Parly had a declaration to make this week: "Cyber war has begun." And she said the Euro nation's military will use its "cyber arms as all other traditional weapons... to respond and attack," as well as setting up a military bug bounty program. From a report: Parly made her pledges during a speech to the Forum International de Cybersecurite (FIC) in the northern French town of Lille. Her speech was on a topic that most Western countries shy away from addressing directly in public. "The cyber weapon is not only for our enemies," said France's defence secretary this afternoon, speaking through a translator. "No. It's also, in France, a tool to defend ourselves. To respond and attack." Her remarks will be seen as moving the debate about offensive cyber capabilities -- not just so-called "active defence" but using infosec techniques as another weapon in the arsenal of state-on-state warfare -- to a new level.
Bitcoin

New Ransomware Strain is Locking Up Bitcoin Mining Rigs in China (zdnet.com) 86

A new strain of ransomware has been observed targeting Bitcoin mining rigs. ZDNet reports: At the time of writing, most of the infections have been reported in China, the country where most of the world's cryptocurrency mining farms are located. Named hAnt, this new ransomware strain was first seen in August of last year, but a new wave of infections has been reported hitting mining farms earlier this month. Most of the infected mining rigs are Antminer S9 and T9 devices, used for Bitcoin mining, but there have also been reports of hAnt infecting Antminer L3 rigs, used for mining Litecoin. In rare instances, Avalon Miner equipment (used for Bitcoin), were also reported as infected, but in much smaller numbers.
Security

More Than Half of PC Applications Installed Worldwide Are Out-of-Date (helpnetsecurity.com) 151

Avast's PC Trends Report 2019 found [PDF] that users are making themselves vulnerable by not implementing security patches and keeping outdated versions of popular applications on their PCs. From a news report: The applications where updates are most frequently neglected include Adobe Shockwave (96%), VLC Media Player (94%) and Skype (94%). The report, which uses anonymized and aggregated data from 163 million devices across the globe, also found that Windows 10 is now installed on 40% of all PCs globally, which is fast approaching the 43% share held by Windows 7. However, 15% of all Windows 7 users and 9% of all Windows 10 users worldwide are running older and no longer supported versions of their product, for example, the Windows 7 Release to Manufacturing version from 2009 or the Windows 10 Spring Creators Update from early 2017.
Security

DHS Issues Security Alert About Recent DNS Hijacking Attacks (zdnet.com) 113

The U.S. Department of Homeland Security has published today an "emergency directive" that contains guidance in regards to a recent report detailing a wave of DNS hijacking incidents perpetrated out of Iran. ZDNet reports: The emergency directive [1, 2] orders government agencies to audit DNS records for unauthorized edits, change passwords, and enable multi-factor authentication for all accounts through which DNS records can be managed. The DHS documents also urges government IT personnel to monitor Certificate Transparency (CT) logs for newly-issued TLS certificates that have been issued for government domains, but which have not been requested by government workers.

The emergency directive comes after last week, the DHS issued an alert about ongoing DNS hijacking attacks through its US-CERT division. The DHS US-CERT alert was based on a report published last week by U.S. cyber-security firm FireEye. The now infamous report detailed a coordinated hacking campaign during which a cyber-espionage group believed to operate out of Iran had manipulated DNS records for the domains of private companies and government agencies. The purpose of these DNS hijacks was to redirect web traffic meant for companies and agencies' internal email servers towards malicious clones, where the Iranian hackers would record login credentials.

Security

Apple's Security Expert Joined the ACLU To Tackle 'Authoritarian Fever' (vice.com) 92

An anonymous reader quotes a report from Motherboard: Apple security expert Jon Callas, who helped build protection for billions of computers and smartphones against criminal hackers and government surveillance, is now taking on government and corporate spying in the policy realm. Jon Callas is an elder statesman in the world of computer security and cryptography. He's been a vanguard in developing security for mobile communications and email as chief technology officer and co-founder of PGP Corporation -- which created Pretty Good Privacy, the first widely available commercial encryption software -- and serving the same roles at Silent Circle and Blackphone, touted as the world's most secure Android phone.

As a security architect and analyst for Apple computers -- he served three stints with the tech giant in 1995-1997, 2009-2011, and 2016-2018 -- he has played an integral role in helping to develop and assess security for the Mac and iOS operating systems and various components before their release to the public. His last stretch there as manager of a Red Team (red teams hack systems to expose and fix their vulnerabilities) began just after the FBI tried to force the tech giant to undermine security it had spent years developing for its phones to break into an iPhone belonging to one of the San Bernardino shooters. But after realizing there's a limit to the privacy and surveillance issues technology companies can address, Callas decided to tackle the issues from the policy side, accepting a two-year position as senior technology fellow for the American Civil Liberties Union. Callas spoke to Motherboard about government backdoors, the need for tech expertise in policymaking, and what he considers the biggest challenge for the security industry.

IT

MacBook Pro Stage Light Fault: Apple's Design Turns $6 Fix Into a $600 Nightmare (9to5mac.com) 166

An anonymous reader shares a report: Some MacBook Pro owners have complained of a 'stage light' effect, where they see uneven backlighting at the bottom of the display. For some, the symptom is only the first stage, with the backlight failing altogether. iFixit says that it has identified the cause -- and the way in which Apple changed the design of the Touch Bar generation for the MacBook Pro turns what would otherwise be a $6 fix into a $600 nightmare. The problem, says the company, is caused by Apple using much thinner ribbon cables instead of the thicker wires used in previous generation MacBook Pro models.
Security

New Phobos Ransomware Exploits Weak Security To Hit Targets Around the World (zdnet.com) 30

An anonymous reader quotes a report from ZDNet: A prolific cybercrime gang behind a series of ransomware attacks is distributing a new form of the file-encrypting malware which combines two well known and successful variants in a series of attacks against businesses around the world. Dubbed Phobos by its creators, the ransomware first emerged in December and researchers at CoveWare have detailed how it shares a number of similarities with Dharma ransomware.

Like Dharma, Phobos exploits open or poorly secured RDP ports to sneak inside networks and execute a ransomware attack, encrypting files and demands a ransom to be paid in bitcoin for returning the files, which in this case are locked with a .phobos extension. The demand is made in a ransom note -- and aside from 'Phobos' logos being added to the ransom note, it's exactly the same as the note used by Dharma, with the same typeface and text use throughout. Phobos is being distributed by the gang behind Dharma and likely serves as an insurance policy for malicious campaigns, providing attackers with a second option for conducting attacks, should Dharma end up decrypted or prevented from successfully extorting ransoms from victims.

Botnet

We'll Likely See a Rise in Internet Blackouts in 2019 (newamerica.org) 58

We'll likely see a rise in internet blackouts in 2019, for two reasons: countries deliberately "turning off" the internet within their borders, and hackers disrupting segments of the internet with distributed denial-of-service (DDoS) attacks. Above all, both will force policymakers everywhere to reckon with the fact that the internet itself is increasingly becoming centralized -- and therefore increasingly vulnerable to manipulation, making everyone less safe. From a report: The first method -- states deliberately severing internet connections within their country -- has an important history. In 2004, the Maldivian government caused an internet blackout when citizens protested the president; Nepal similarly caused a blackout shortly thereafter. In 2007, the Burmese government apparently damaged an underwater internet cable in order to "staunch the flow of pictures and messages from protesters reaching the outside world." In 2011, Egypt cut most internet and cell services within its borders as the government attempted to quell protests against then-President Hosni Mubarak; Libya then did the same after its own unrest.

In 2014, Syria had a major internet outage amid its civil war. In 2018, Mauritania was taken entirely offline for two days when undersea submarine internet cables were cut, around the same time as the Sierra Leone government may have imposed an internet blackout in the same region. When we think about terms like "cyberspace" and "internet," it can be tempting to associate them with vague notions of a digital world we can't touch. And while this is perhaps useful in some contexts, this line of thinking forgets the very real wires, servers, and other hardware that form the architecture of the internet. If these physical elements cease to function, from a cut wire to a storm-damaged server farm, the internet, too, is affected. More than that, if a single entity controls -- or can at least access -- that hardware for a region or even an entire country, government-caused internet blackouts are a tempting method of censorship and social control.

Privacy

Online Casino Group Leaks Information on 108 Million Bets, Including User Details (zdnet.com) 13

An online casino group has leaked information on over 108 million bets, including details about customers' personal information, deposits, and withdrawals, ZDNet has learned. From the report: The data leaked from an ElasticSearch server that was left exposed online without a password, Justin Paine, the security researcher who discovered the server, told ZDNet. ElasticSearch is a portable, high-grade search engine that companies install to improve their web apps' data indexing and search capabilities. Last week, Paine came across one such ElasticSearch instance that had been left unsecured online with no authentication to protect its sensitive content. From a first look, it was clear to Paine that the server contained data from an online betting portal.

[...] After an analysis of the URLs spotted in the server's data, Paine and ZDNet concluded that all domains were running online casinos where users could place bets on classic cards and slot games, but also other non-standard betting games. Some of the domains that Paine spotted in the leaky server included kahunacasino.com, azur-casino.com, easybet.com, and viproomcasino.net, just to name a few.

Security

Bug Bounties Aren't Silver Bullet for Better Security (infosecurity-magazine.com) 95

Many organizations may find they're better off hiring pen testers and in-house security researchers directly than running bug bounty programs, according to new MIT research. From a report: The New Solutions for Cybersecurity paper features a surprising analysis of bug bounty programs in the chapter, Fixing a Hole: The Labor Market for Bugs. It studied 61 HackerOne bounty programs over 23 months -- including those run for Twitter, Coinbase, Square and other big names -- and one Facebook program over 45 months. It claimed that, contrary to industry hype, organizations running these programs don't benefit from a large pool of white hats probing their products. Instead, an elite few produce the biggest volume and highest quality of bug reports across multiple products, earning the biggest slice of available rewards. It's also claimed that even these elite "top 1%" ethical hackers can't make a decent wage by Western standards.
Music

MIDI Association Announces MIDI 2.0 Prototyping (hackaday.com) 133

MIDI was introduced at the 1983 NAMM show as a means to connect various electronic instruments together. Since then, our favorite five-pin DIN has been stuffed into Radio Shack keyboards, MPCs, synths, eurorack modules, and DAWs. The standard basically hasn't changed. Now, ahead of the 2019 NAMM show, the MIDI Manufacturers Association (MMA) in conjunction with AMEI, Japan's MIDI Association, are announcing MIDI 2.0. From a report: The new features include, "auto-configuration, new DAW/web integrations, extended resolution, increased expressiveness, and tighter timing." It will retain backwards-compatibility with MIDI 1.0 devices. The new initiative, like the release of the first MIDI spec, is a joint venture between manufacturers of musical instruments. The company lineup on this press release is as follows: Ableton/Cycling '74, Art+Logic, Bome Software, Google, imitone, Native Instruments, Roland, ROLI, Steinberg, TouchKeys, and Yamaha.
Security

Popular WordPress Plugin WPML Hacked By Angry Former Employee (zdnet.com) 37

A very popular WordPress plugin was hacked over the weekend after a hacker defaced its website and sent a mass message to all its customers revealing the existence of supposed unpatched security holes. From a report: In a follow-up mass email, the plugin's developers blamed the hack on a former employee, who also defaced their website. The plugin in question is WPML (or WP MultiLingual), the most popular WordPress plugin for translating and serving WordPress sites in multiple languages. According to its website, WPML has over 600,000 paying customers and is one of the very few WordPress plugins that is so reputable that it doesn't need to advertise itself with a free version on the official WordPress.org plugins repository. But on Saturday, ET timezone, the plugin faced its first major security incident since its launch in 2007. The attacker, which the WPML team claims is a former employee, sent out a mass email to all the plugin's customers.
Security

Firmware Vulnerability In Popular Wi-Fi Chipset Affects Laptops, Smartphones, Routers, Gaming Devices (zdnet.com) 100

Embedi security researcher Denis Selianin has discovered a vulnerability affecting the firmware of a popular Wi-Fi chipset deployed in a wide range of devices, such as laptops, smartphones, gaming rigs, routers, and Internet of Things (IoT) devices. According to Selianin, the vulnerability impacts ThreadX, a real-time operating system that is used as firmware for billions of devices. ZDNet reports: In a report published today, Selianin described how someone could exploit the ThreadX firmware installed on a Marvell Avastar 88W8897 wireless chipset to execute malicious code without any user interaction. The researcher chose this WiFi SoC (system-on-a-chip) because this is one of the most popular WiFi chipsets on the market, being deployed with devices such as Sony PlayStation 4, Xbox One, Microsoft Surface laptops, Samsung Chromebooks, Samsung Galaxy J1 smartphones, and Valve SteamLink cast devices, just to name a few.

"I've managed to identify ~4 total memory corruption issues in some parts of the firmware," said Selianin. "One of the discovered vulnerabilities was a special case of ThreadX block pool overflow. This vulnerability can be triggered without user interaction during the scanning for available networks." The researcher says the firmware function to scan for new WiFi networks launches automatically every five minutes, making exploitation trivial. All an attacker has to do is send malformed WiFi packets to any device with a Marvell Avastar WiFi chipset and wait until the function launches, to execute malicious code and take over the device.
Selianin says he also "identified two methods of exploiting this technique, one that is specific to Marvell's own implementation of the ThreadX firmware, and one that is generic and can be applied to any ThreadX-based firmware, which, according to the ThreatX homepage, could impact as much as 6.2 billion devices," the report says. Patches are reportedly being worked on.
Democrats

Russian Hackers Allegedly Attempted To Breach the DNC After the 2018 Midterms (fortune.com) 127

An anonymous reader quotes a report from Fortune: Russian hackers attempted to breach Democratic National Committee email addresses in a spear-phishing campaign just after the 2018 midterms, according to a DNC court document filed Thursday night. "The content of these emails and their timestamps were consistent with a spear-phishing campaign that leading cybersecurity experts have tied to Russian intelligence," reads the complaint. "Therefore, it is probable that Russian intelligence again attempted to unlawfully infiltrate DNC computers in November 2018." The complaint [...] said there is no evidence that the attempted hack in Nov. 2018 was successful.

Spear-phishing campaigns involve sending emails that appear to be from a trusted source in order to gain confidential information. According to CNN, the emails in question appeared to have been sent from a State Department official and contained a PDF attachment that, if opened, would allow the hacker access to the recipient's computer. The timing and content of these emails were consistent with the practices of the Russian hacking group known as Cozy Bear, one of the two groups that hacked the DNC prior to the 2016 U.S. presidential election. According to the cybersecurity firm FireEye, Cozy Bear attempted to hack over 20 entities in Nov. 2018, including clients in local government, transportation, defense, law enforcement, and military.

Firefox

Firefox To Remove UI Dark Pattern From Screenshot Tool After Months of Complaints (zdnet.com) 127

After months of user complaints, Mozilla will remove a misleading "dark pattern" from its page screenshot utility. From a report: The problematic feature is the "Save" button that appears when Firefox users take a screenshot. The issue is that the Save button doesn't save the screenshot to the PC, as most users would naturally expect, but uploads the image to a Mozilla server. This is both a privacy violation, as some users don't appreciate being tricked into uploading sensitive images saved on remote servers, but also an incovenience as users would still have to download the image locally, but in multiple steps afterward.
Spam

Verizon Will Give Subscribers Free Access To Anti-Robocall Tools (engadget.com) 40

Verizon says it will give all its subscribers free access to its spam alert and call blocking tools, so long as their phones can support the features. From a report: The carrier originally rolled out those tools over a year ago as part of its $3-per-month Call Filter add-on. But starting in March, subscribers with compatible smartphones (including iPhone and Android devices) will be able fend off unwanted robocalls without having to pay extra. Verizon says it will release more info on how to sign up for the free tools near their launch date.
Security

That 773M Password 'Megabreach' is Years Old (krebsonsecurity.com) 29

Security reporter Brian Krebs writes: My inbox and Twitter messages positively lit up today with people forwarding stories from Wired and other publications about a supposedly new trove of nearly 773 million unique email addresses and 21 million unique passwords that were posted to a hacking forum. A story in The Guardian breathlessly dubbed it "the largest collection ever of breached data found." But in an interview with the apparent seller, KrebsOnSecurity learned that it is not even close to the largest gathering of stolen data, and that it is at least two to three years old.

The dump, labeled "Collection #1" and approximately 87GB in size, was first detailed earlier today by Troy Hunt, who operates the HaveIBeenPwned breach notification service. Hunt said the data cache was likely "made up of many different individual data breaches from literally thousands of different sources." KrebsOnSecurity sought perspective on this discovery from Alex Holden, CTO of Hold Security, a company that specializes in trawling underground spaces for intelligence about malicious actors and their stolen data dumps. Holden said the data appears to have first been posted to underground forums in October 2018, and that it is just a subset of a much larger tranche of passwords being peddled by a shadowy seller online.

Slashdot Top Deals